in Barcelona
 3 to 5 Nov 2026
The UK has implemented a law prohibiting IoT manufacturers from setting weak default passwords like “admin” or “12345” to bolster cybersecurity. This move aims to avert incidents like the 2016 Mirai hack, where poor password security enabled a massive botnet attack. Manufacturers must now also disclose contact details for reporting issues and inform users about upcoming security updates. Non-compliance could lead to fines up to £10 million or 4% of global revenue. While the EU is considering similar legislation, the U.S. currently lacks specific provisions against weak default IoT passwords.
From Kurrant


Live panel
 Making sense of city lighting data
How lighting standards drive unification and interoperability
Making sense of city lighting data
How lighting standards drive unification and interoperability
 Jonathan CatchpoleChairman, Zhaga Technical Coordination Workgroup
 José SanchisChairman, TALQ Certification Workgroup
 Paul DrosihnGeneral Manager, DALI Alliance
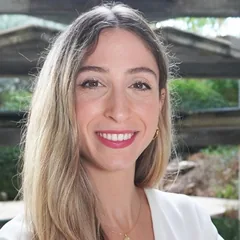 Emma Lozano DooganModerator, Kurrant
Wed 4 Nov13:30
Kurrant boothPavilion 3, Booth D151 · Barcelona
Add to calendar
Kurrant Tender Tracker
Never miss a smart city and utility tender
Start 3 months freeGet tender alerts
Related news
Latest news
Kurrant Originals
Recent event coverage
Featured Case Studies
Real client work behind the news. Strategy, M&A and engineering projects we've delivered for cities and utilities.